
DropEnv is a developer tool for sharing environment variables through temporary links, with encryption performed in the browser.
Why I built it
Sharing a .env file with a teammate sounds harmless until you remember what those files contain. DropEnv was my attempt to make that exchange less risky: encrypt the contents in the browser, keep the decryption key in the URL fragment, and give shared data a limited lifetime. Building it pushed me to learn the Web Crypto API beyond simply following an example.
| Year | 2025 |
| Type | Developer tool |
| Client | Personal project |
| My role | Design, encryption |
| Platform | Web |
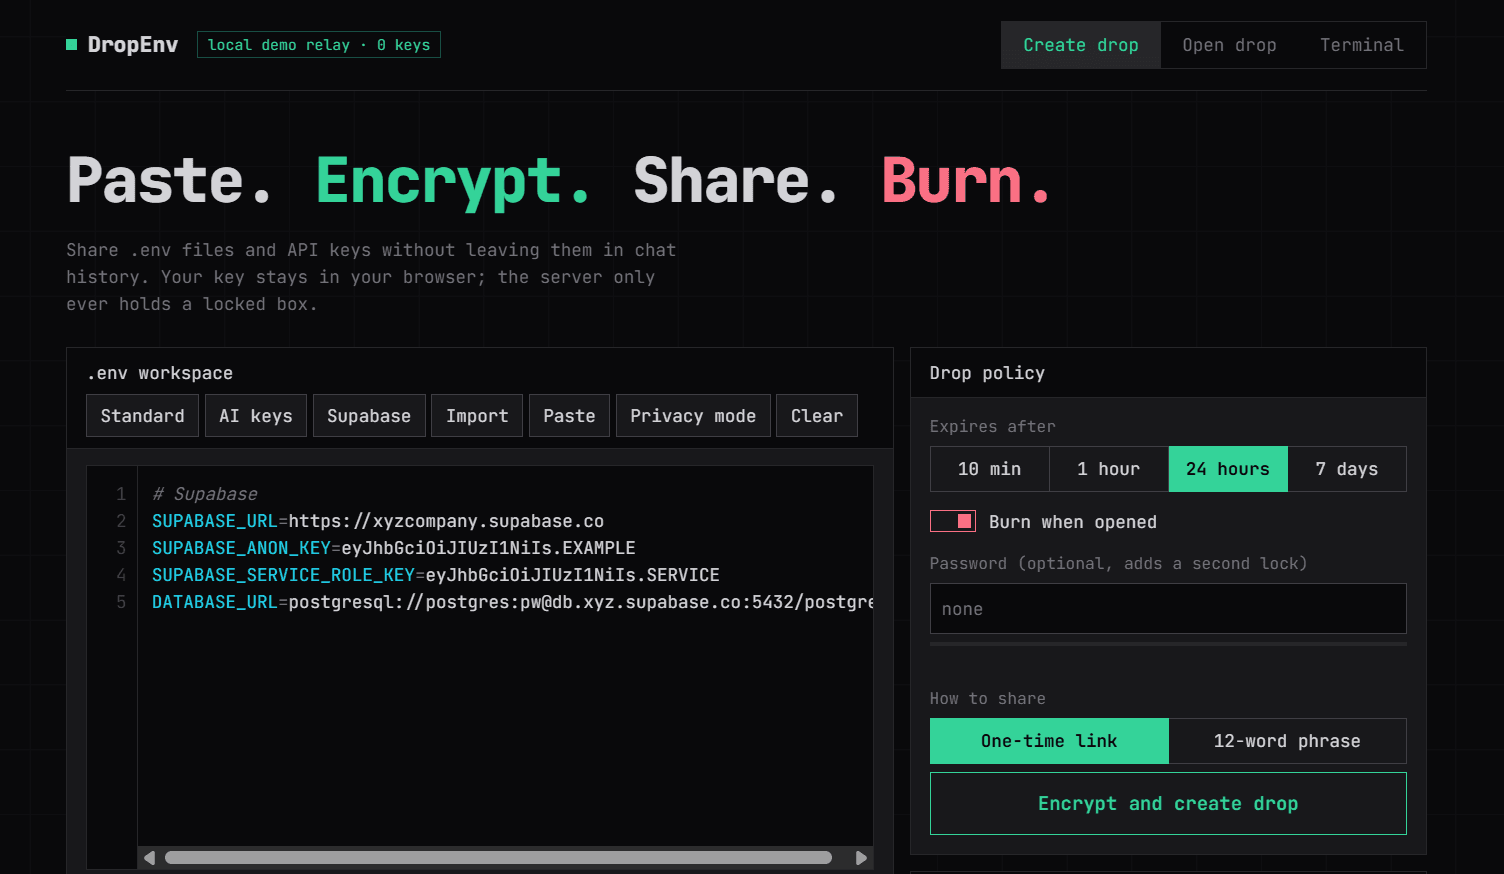
Instead of sending configuration values as plain text in a chat, the tool encrypts the contents client-side before sharing them. The design keeps the decryption key in the URL fragment rather than the normal HTTP request.
Challenge
The core challenge was handling encryption and decryption in the browser while managing temporary links, expiration, and view limits. Security also required understanding exactly which parts of the data and key each component could access.
Action
Browser-side AES-GCM encryption
I used the Web Crypto API with AES-GCM to encrypt shared content in the browser. The decryption key is stored in the URL fragment, which is not included in the HTTP request sent to the server.
Temporary access and expiry
I implemented link expiration and view limits to control how long shared content remains available. These controls reduce the lifetime of a share but do not replace secure handling of the link itself.
Result
DropEnv gave me practical experience with browser cryptography, temporary resource lifecycles, and the security trade-offs involved in sharing sensitive configuration data.